Secure agent access with 1Password + NVIDIA OpenShell
Today we’re introducing 1Password for NVIDIA OpenShell, available now as a developer preview in the 1Password nightly build. You can set up and connect a 1Password Environment to the OpenShell runtime, which lets your agents work with the systems they need without exposing real credentials to the underlying model.
Agentic workflows introduce a fundamental security challenge: credentials. An agent needs access to repositories, APIs, and internal services to complete complex tasks, but a long-lived secret grants broader, more persistent access than necessary. Developers need a way to give agents access only where it’s approved and for as long as it’s needed.
How it works
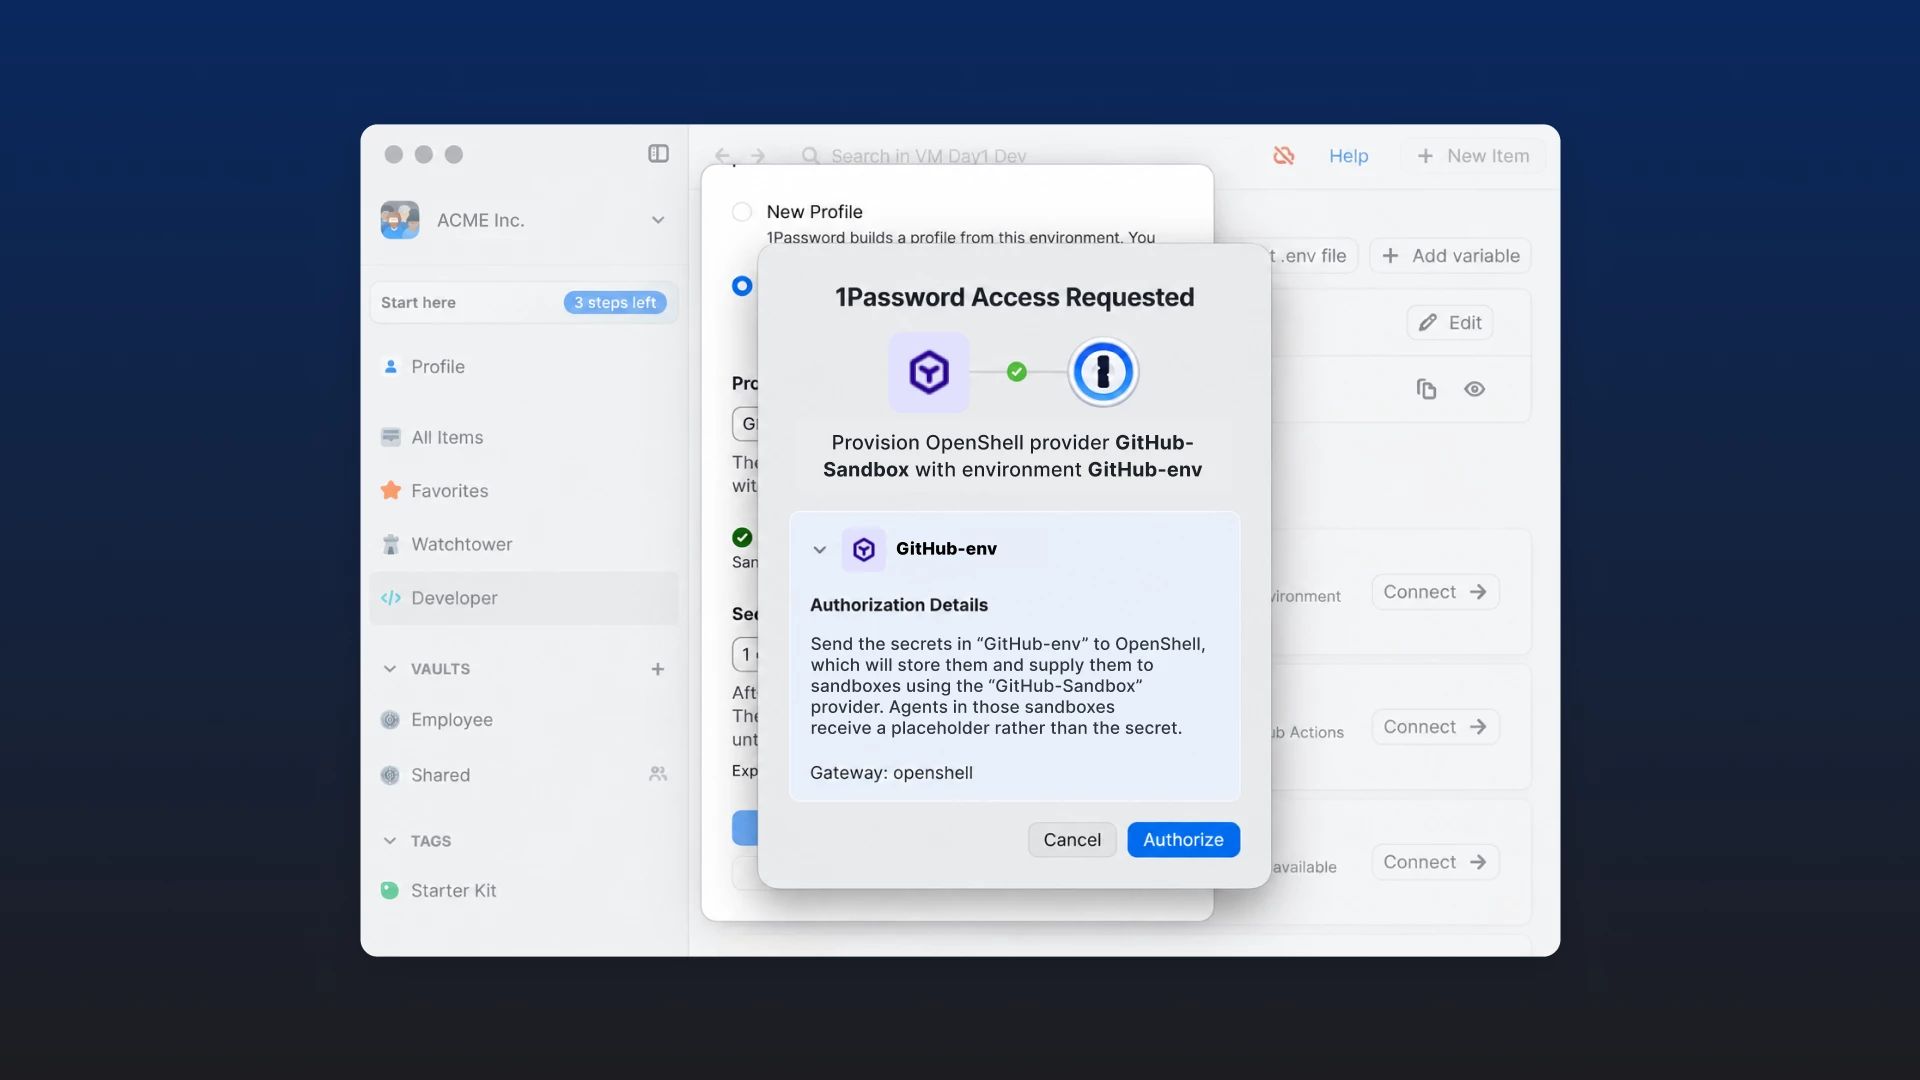
1Password for NVIDIA OpenShell extends 1Password’s secrets management workflow through 1Password Environments. It gives developers a dedicated place to organize the variables an agent needs, separate from personal passwords and shared team credentials. You can map an Environment to an OpenShell Provider Profile, choose the destinations where credentials can be used, set an expiration date and time, and specify whether the sandbox can read or write. Crucially, you’re able to review and authorize the connection before the agent starts work.
Once the provider is attached to an OpenShell sandbox, OpenShell has custody of the credentials for the time you’ve set. Inside the sandbox, the agent sees placeholders rather than real credentials. OpenShell Gateway resolves a value when the agent sends a request to an approved host, and stops resolving it after access expires.
Get started by setting up the integration. You can also read the full announcement for more details. Let us know your experience and what you’re building down in the comments!