adfhogan
September 28, 2026
Question

How many different sites does an application support forum need to pull in Javascript from?

  • September 28, 2026
  • 2 replies
  • 12 views

By default, I have my browser set up to block ads, and to screen javascript from sites until it’s whitelisted.

This forum seems to require more javascript than most news websites to run..
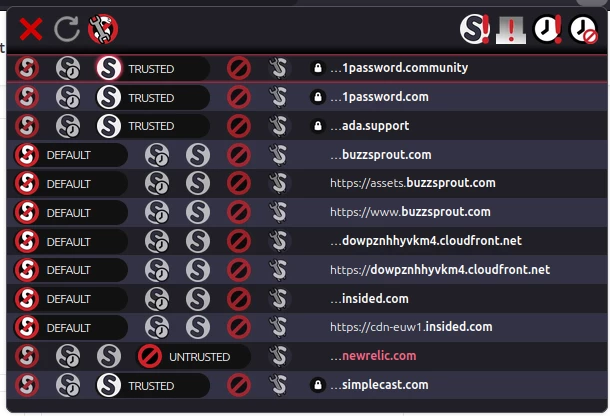
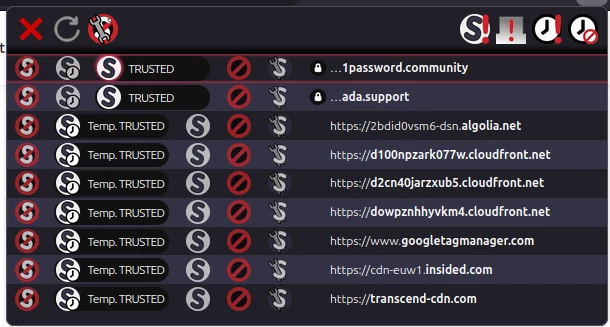
First two passes
Second pass

Now, I get that SaaS and all that, things need to bring in resources from other places - but surely for a security focused business - you don’t need all this?

1password.community = your site (obvs)
ada.support = AI powered CS automation platform
algolia.net = AI search and retrieval platform
buzzsprout.com = podcast and RSS hosting
simplecast.com = podcast hosting/distribution, analytics
cloudfront.net = AWS CDN
googletagmanager.com = Google webstats
insided.com = CS community platform
transcend-cdn.com = data privacy and compliance platform (cookie manager)
newrelic.com = Cloud “observability and app performance” (stats/monitoring)
 

Do you really need all of this to run a messageboard? … and if you do need a lot of it, surely they provide CNAME capability for some of it, so it’s clear it’s something you’ve intended.

2 replies

KG4ZOW
September 28, 2026

I’m using uMatrix to block javascript until I approve it, I’m seeing almost the same thing.

The dark green entries are the ones I had to allow, just to make the site (and the login process) usable.

1P_SimonH
Community Manager
Community Manager
September 28, 2026

Hey ​@adfhogan 👋

Thanks for raising this, and for the detail you put into it. You did some good detective work on each service! It's a fair question to ask, especially of a security company.

The community runs on a third-party platform rather than something we built in-house, so a number of those domains come as part of that platform. The rest are things we've deliberately added. Everything in that list went through our internal security and privacy review before it was switched on.

I’d actually welcome your opinion on the CNAME configuration. Routing these through our own subdomains would make it obvious the requests are intentional, which is useful. But it would also mean the hostname no longer tells you who's actually providing the code, and we'd be making it less obvious that these are third-party services.

Our instinct has been that visible is better than tidy, even when visible invites threads like this one. But you're clearly thinking about this carefully, so: which would you rather have as a user? Fewer unfamiliar domains and a clear signal that everything is deliberate, or the current setup where you can see exactly who each request is going to and judge for yourself? Would welcome your thoughts on this too, ​@KG4ZOW.

And regardless of where that lands: please keep using whatever tools suit you to optimize your browsing experience.