Sep 22, 2026 1:39 PM UTC

User verification when signing in with a passkey

Hi, something appears to have changed in the 1Password Chrome extension (macOS).

Passkeys used to be fillable without being prompted for biometrics. As I use my laptop with the lid closed, I have to enter my macOS account password now each time I want to use a Passkey, which is… really annoying.

It doesn’t matter if 1Password is locked, unlocked, there’s no cooldown on this, it prompts _every_ time and I cannot find a setting to correct this.

This seems to be a regression. I’d love it if someone has a fix.

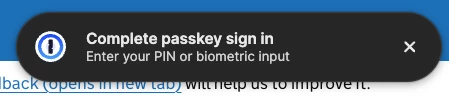
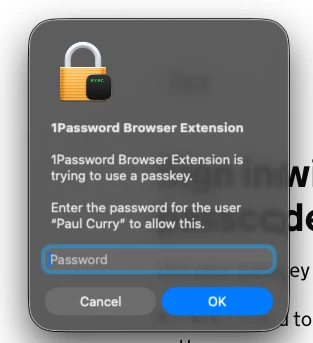
Screenshots of the problem below.

Strings for search: “1Password Browser Extension is trying to use a passkey”, “Complete passkey sign in”, “Enter your PIN or biometric input”.

This did not happen before. This is new behaviour and is detrimental.
 

Pinned Reply By 1P_Dave

Hello ​@cr3! 👋

Thanks for reaching out! Whenever you visit a protected site, 1Password now checks the authentication level requested by the site and prompts you for additional verification when needed. This helps ensure that passkeys grant the right access to the right person every time.

Whether additional user verification is required is determined by the website that you’re signing into and not 1Password. 1Password just respects the authentication level that is enforced by the website in question.

That being said, our team will continue to work with our friends at the FIDO Alliance to make saving and signing in with passkeys as convenient as possible and all of your feedback is being tracked internally. 

-Dave

13 replies

1P_Dave
1Password Employee
1P_DavePinned
1Password Employee
Sep 22, 2026 5:49 PM UTC

Hello ​@cr3! 👋

Thanks for reaching out! Whenever you visit a protected site, 1Password now checks the authentication level requested by the site and prompts you for additional verification when needed. This helps ensure that passkeys grant the right access to the right person every time.

Whether additional user verification is required is determined by the website that you’re signing into and not 1Password. 1Password just respects the authentication level that is enforced by the website in question.

That being said, our team will continue to work with our friends at the FIDO Alliance to make saving and signing in with passkeys as convenient as possible and all of your feedback is being tracked internally. 

-Dave

Oct 5, 2026 4:45 PM UTC

This is an unacceptable change in behavior and a massive regression in UX. I understand why you do this, but leaving us no choice in the matter is what makes it unacceptable. Having to enter my macOS account password each and every time I want to sign in using a passkey entirely defeats the purpose of storing passkeys in 1Password - which is already unlocked using my master password. 

This is basically a tripple-authentication flow. 

To make matters worse, you force the entire process into your new Sign-In “experience”, even when that is turned off. People turn the new sign-experience off for a reason, and that setting should be respected. 

cr3Author
Sep 22, 2026 5:54 PM UTC

Thanks for the answer, that is at least clear. It is not a desirable behaviour; this is making sign in more difficult for websites that can now request this. But, if there is no plan to offer configuration to go back to the previous behaviour, I guess we’re gonna have to live with it.

MattSuda
Sep 23, 2026 9:40 AM UTC

Passkeys previously worked great for a long time with 1 click in the browser, please add a setting so we can go back to 1 click login with passkeys.

For some people the extra passkey security is great, but I’ve already unlocked my Mac and 1Password, so I should be able to continue logging in with passkeys with 1 click. This is a major downgrade to the ease of use. So exhausting having to lift my hand away from keyboard and mouse to use the TouchID sensor on Mac. 1Password used to be about ease of use, but lately there’s been so many extra steps just to login now. It’s so annoying having to use TouchID or Mac password to login to every website.

Respecting the website wanting to verify passkeys has little impact on the user on an iPhone with the quick FaceID, however on a Mac it downgrades the ease of use.

Because of this, I along with other users will now just downgrade back to using username and passwords for all of our logins because of the ease of use with 1 click login.

1P_Dave
1Password Employee
1Password Employee
Sep 23, 2026 2:00 PM UTC

​@MattSuda 

This is us adopting the passkey user verification standard. It allows a website to request additional authentication when a passkey is used, and we now respect the level of verification the website requires. This helps websites confirm how a passkey was authenticated and ensures they can continue to support saving passkeys in 1Password.

-Dave

cr3Author
Sep 23, 2026 2:09 PM UTC

I would argue that if the current 1Password session has been biometrically authenticated once, it should not pop every time, even if the site requests it. 1Password can happily attest “yes, that’s the user”. We have various options to lock automatically lock 1Password to our own comfort.

From the spec, depending which you are citing, the intent of Passkey User Verification is “...to distinguish individual users”, which the 1Password session is already aware of and can attest to.

In essence, I disagree with 1P’s interpretation of the spec. It is surprisingly user unfriendly.

Sep 23, 2026 6:16 PM UTC

I agree with the “user unfriendly” part. I am using a password manager, so I don’t have to type in passwords all the time. The new behavior defeats this purpose.

Even more, if I need to (re)authenticate each time I want to use a passkey, but at the same time I can still use “classic” username/password/OTP authentication without doing so, I see some hard times ahead for the wide adoption of passkeys.

As the only user on my personal Mac, I want to have at least the choice to ignore the website’s “requirements”. Make it optional, maybe give corporate admins the ability to force the setting for corporate accounts.

Sep 28, 2026 6:16 AM UTC

This needs to be changed. Every time I sign in with a passkey on my Mac, I get two boxes. First Apple's box asks me to click Continue. Then a second box says the site "requires authentication for this passkey" and makes me type my Mac password. It does this in both Edge and Safari.

The ironic thing is that I sign in to the same site with the same passkey in 1Password on Windows and it doesn't ask for anything. Same product, but you don’t follow the site’s request in Windows?  On Mac the site asks for verification and I have to type my Mac password every time, after already clicking through Apple's box.

I'm already signed in to 1Password. That should be enough. If the vault is unlocked, the site should just get the passkey. Making me type my computer password every time is annoying, and it makes passkeys worse than a regular password with autofill.
 

Oct 3, 2026 8:13 PM UTC

Adding my voice here. This change has made passkeys meaningfully worse than passwords for me, which seems like the opposite of what 1Password is trying to achieve.

As of this week, every passkey sign-in in Chrome on macOS triggers the system prompt ("1Password Browser Extension is trying to use a passkey") and asks for my Mac password. It happens every single time: whether 1Password is locked or unlocked, in a normal or incognito window, with no grace period and no "remember" option.

The result is absurd: signing in with a saved password and OTP is now faster and less friction than using the passkey. I already authenticated to 1Password. Being forced to re-authenticate to macOS on top of that for every login undoes the main reason I use a password manager and the main promise of passkeys.

I understand the intent of honoring a site's user-verification requirement, but there has to be a better balance. A few options that would fix it:

- Treat an unlocked 1Password vault (unlocked with biometrics or my account password) as satisfying user verification for a configurable window
- Add a grace period, e.g. don't re-prompt for X minutes after a successful verification
- Give users a setting to control this behavior

Right now the experience actively pushes me back toward passwords. Please reconsider or make this configurable.

Oct 23, 2026 3:17 AM UTC

Agree with all of the other comments here. This is unacceptable, fundamentally misunderstands the standard, and eliminates the primary advantage to passkeys. This is not something that needs changed at the FIDO alliance, this is 1password misinterpreting the requirement.

This change has me seriously considering abandoning passkeys in favor of password+otp. The change must be reverted or passkey use is going to suffer.

Nov 3, 2026 11:31 PM UTC

I agree with bs87--going back to passwords, as this misinformed implementation by 1Password negates the full benefit of a password manager.

Nov 7, 2026 2:23 PM UTC

Also agree with all of the user comments. I have now stopped using passkeys in favor of userid/password as it is much quicker/easier. As one comment noted, it’s not such a big deal on my iPhone with faceid, but on my Mac it’s totally annoying to have to use touch ID EVERY time I log in to a site. Since all of my hundreds of online services/accounts still have userid/password support, I’ll just go back to using that approach which is a shame. Passkeys are now a pain and shouldn’t be!

Nov 11, 2026 5:04 PM UTC

Agree with all of the other comments here. This is unacceptable, fundamentally misunderstands the standard, and eliminates the primary advantage to passkeys. This is not something that needs changed at the FIDO alliance, this is 1password misinterpreting the requirement.
This change has me seriously considering abandoning passkeys in favor of password+otp. The change must be reverted or passkey use is going to suffer.


+1 to this. This has me forgoing passkeys in situations where they would clearly increase security. The FIDO standard is clearly satisfied by biometric authentication within the 1pw session, rather than only at the instant of login.