Write-only access to environments and avoiding duplication in environment variables
Hey folks!
We're migrating from Heroku to AWS (ECS, Lambda, RDS, etc.) and, at the same time, tightening secret management across all our environments: dev, CI, staging, and production.
Here's what I had in mind:
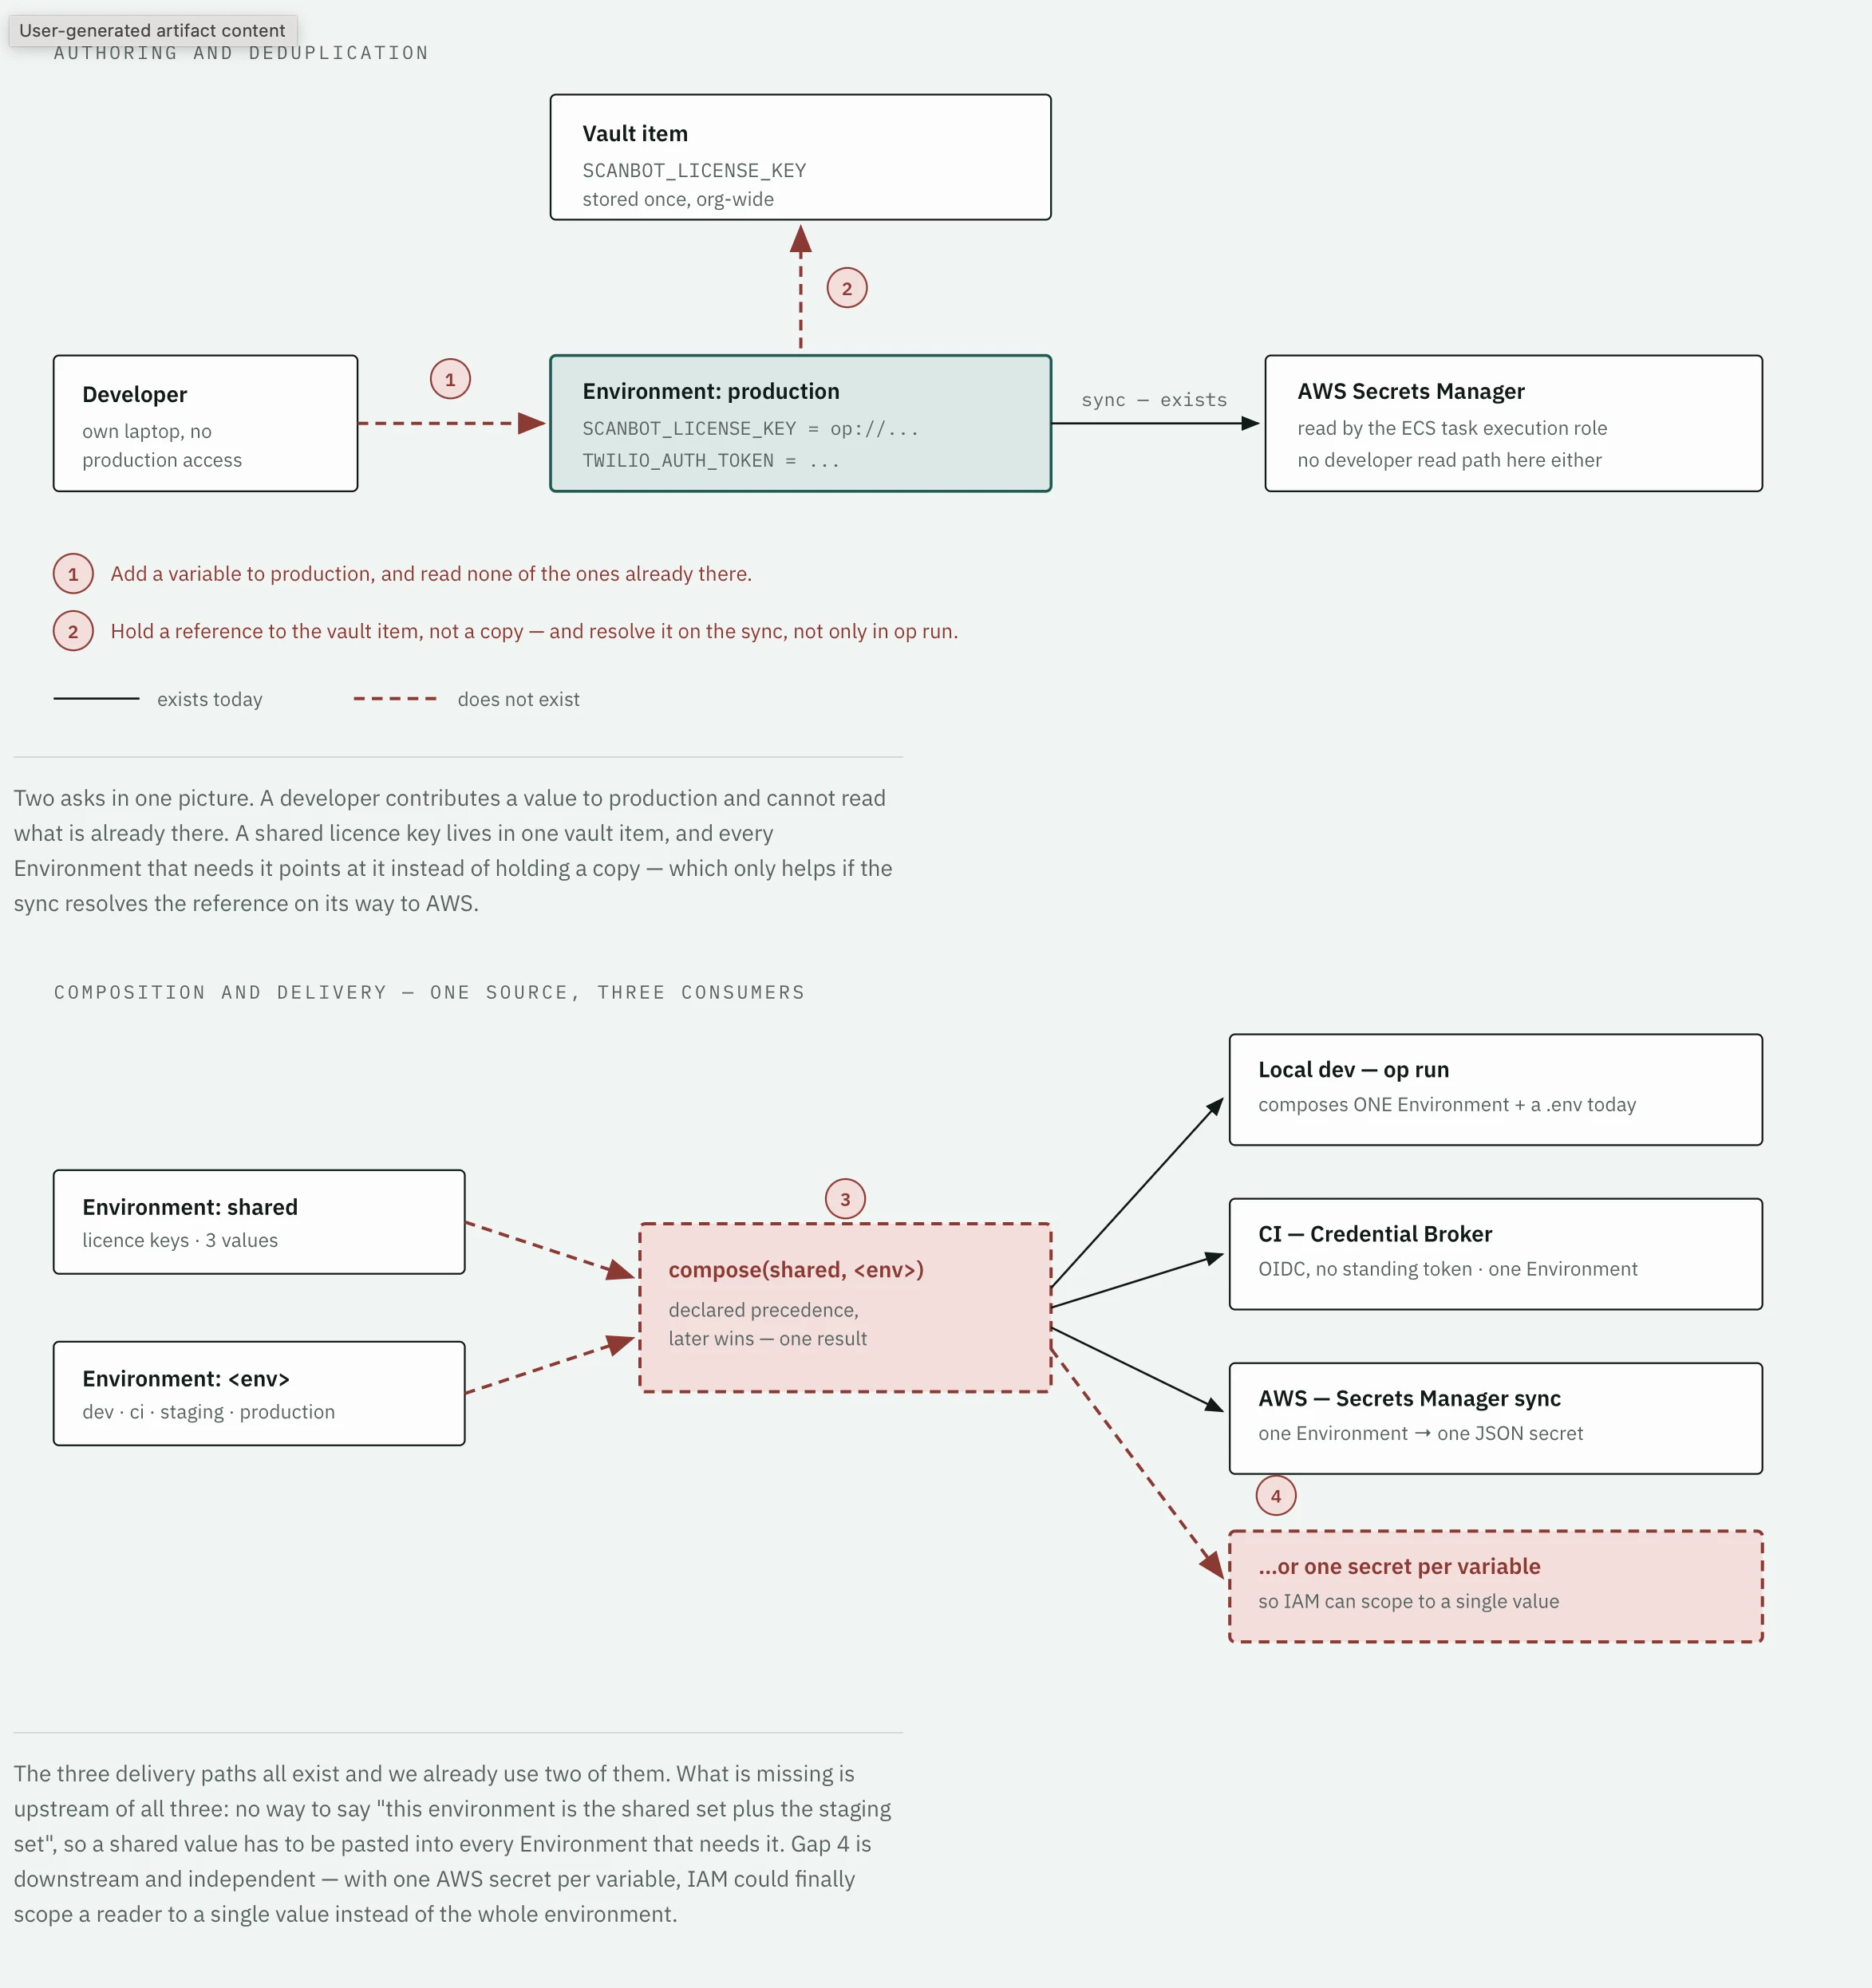
Problem 1: No easy way to deduplicate values. The most obvious example is license keys that are identical across all environments. I see two possible solutions: composition (merging variables from multiple 1Password environments) or letting variables reference vault items. I can probably get composition working on AWS and in local development (by using the 1Password SDK most likely).
Problem 2: Individual secrets instead of a single JSON blob. We use a Terraform platform called Ravion. Its standard modules (ECS, Lambda, etc.) can inject values from SSM and Secrets Manager by key. 1Password puts all values into a single JSON blob. That's workable, but having each value as a separate item would be much better. SSM support would be great too.
Problem 3: No write-only access to production. Our developers work mostly full-stack and need to be able to add secrets in every environment. But for basic security hygiene, I'd like to limit full access to admins and whoever is on call. As far as I know, there's no way to grant write-only (or, even better, create-only) permissions. My workaround was to let developers push new secrets to an intermediate vault or environment and have a CI workflow promote them to production. Unfortunately, your service accounts can't write to environments.
Any suggestions or feedback are appreciated!